I was drawn to national security through my first job at CyberProtex, where they gave me hands-on experience with tooling used in the government, cybersecurity evaluations, and real-world experience with writing software.
Huntsville, AL
May 2024 – Present · Huntsville, AL
CyberProtex
Junior Security Software Engineer
My technical range is diverse from my experience utilizing Python, LAMP stacks, PostgreSQL, REST and OAuth 2.0, Microsoft Sentinel, and Fortify SAST during my time at CyberProtex.
Enterprise clients
8 → 19Enterprise clients
Users
200+Users
Saved per audit
~720 hrsSaved per audit
Defender events triaged
200,000+Defender events triaged
This work is for a government client, so it's shown in text and diagrams only. No screenshots, client names, or addresses.
At CyberProtex
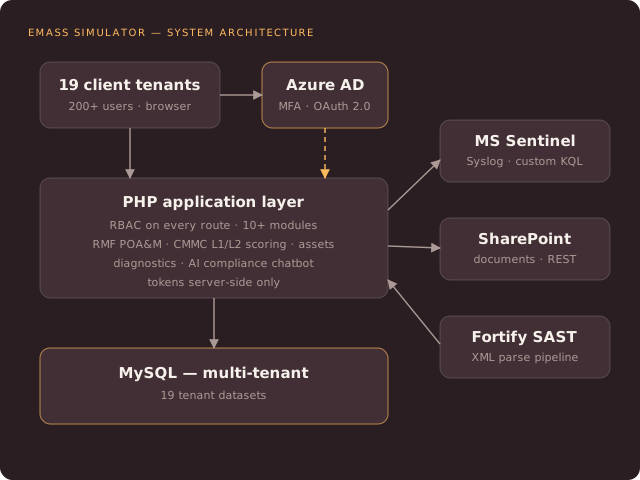
Architecture only. No client data, names or addresses.
eMASS Simulator
PHP · MySQL · Docker · RMF · CMMC
Developed eMASS Simulator, a full-stack compliance web app (PHP, MySQL, Docker), adopted by 19 enterprise clients (up from 8) and 200+ users, saving ~720 hours per audit.
I managed and built out the eMASS Simulator on a LAMP stack using a SQL database with REST APIs and OAuth 2.0 for a Microsoft authenticator integration upon logins.
In the eMASS Simulator I constructed numerous automated reports based on mass quantities of data that would be filtered through a pipeline and shown on a dashboard for clients.
PHP
MySQL
RMF
CMMC
NIST 800-53
0/71on VirusTotallater confirmed by Microsoft
Ransomware alert triage
Microsoft Defender for Endpoint · VirusTotal · Sysinternals
Triaged 200,000+ Microsoft Defender security events during a suspected ransomware attack and proved it was a false alarm, preventing a company-wide escalation.
By utilizing the MD5 hash of the file, we swiftly searched VirusTotal's online database and found that it was not found positive for any threats (0/71).
This led us to suspect it was most likely a false alert on a non-whitelisted Datto RMM update, but to ensure that it actually was a false positive, we manually went in and checked defender logs, Sysinternals, and other virus detection systems on both the alerted files and the overall system.
Our suspicion was later confirmed by Microsoft in a public announcement.
Illustration of a severity workbook — not client data.
Syslog into Microsoft Sentinel
Linux · Syslog · Sentinel · KQL
Architected a Syslog ingestion pipeline forwarding Ubiquiti firewall logs into Microsoft Sentinel with severity-based data collection rules, authoring custom KQL workbooks for real-time threat detection.
I built out a custom syslog server to intake Ubiquiti logs and forward them to a Microsoft Sentinel database and displayed it with KQL and Microsoft Workbooks.
Sentinel
KQL
Syslog
Ubiquiti
110NIST 800-171 practices
CMMC assessment engine
CMMC Level 1 & 2 · NIST SP 800-171
Built an automated assessment engine that scores companies against 110 federal security requirements (NIST 800-171), replacing manual audit review for 19 client organizations.
NIST 800-171
CMMC
Automation
200+accounts across 19 client tenants
Account security
Microsoft Entra ID · SharePoint
Hardened account security across 200+ accounts and 19 client tenants by integrating SharePoint document libraries via REST API and OAuth 2.0, enforcing MFA through Microsoft Entra ID.
Built ShiftSplit, the company's timesheet and billing app (PHP, MySQL, Zoho API over OAuth 2.0), logging 450+ hours every two weeks across 340+ client tickets.
Attacked 30+ student teams' networks in HackUCF's 2026 Horse Plinko competition, running custom tomes through Realm and Sliver command-and-control (C2) beacons and JS-Tap implants on Kali Linux.
Red team
Realm
Sliver C2
JS-Tap
Kali Linux
2hardening playbooks: pfSense/FreeBSD and MikroTik RouterOS
pfSense and MikroTik hardening playbooks
pfSense · FreeBSD · MikroTik RouterOS
Authored pfSense/FreeBSD and MikroTik RouterOS hardening playbooks used by the team for competition prep; also competed in ICEAGE and on the UCF CCDC C3 training roster team.
Through HackUCF I've gained substantial knowledge regarding terminology, procedures, OS, Docker, and other security features.